A Microsoft 365 account hacked incident needs more than a password reset. An attacker may have left behind a quiet way to watch, hide, redirect, or delete email after the user regains access. Silent mailbox rules often provide some of the clearest clues about what happened, what the attacker wanted, and whether the risk may still be active.
When we investigate these incidents, we look beyond the login itself. Mailbox rules can expose targeted fraud plans, data collection efforts, and attempts to keep the real user from seeing security alerts or payment messages. Reviewing them quickly helps us preserve the story before important evidence disappears.
Why Silent Mailbox Rules Matter
Mailbox rules are normal tools. Users may create them to sort newsletters, organize project messages, or forward approved business communications. The problem begins when an attacker creates or changes a rule without permission.
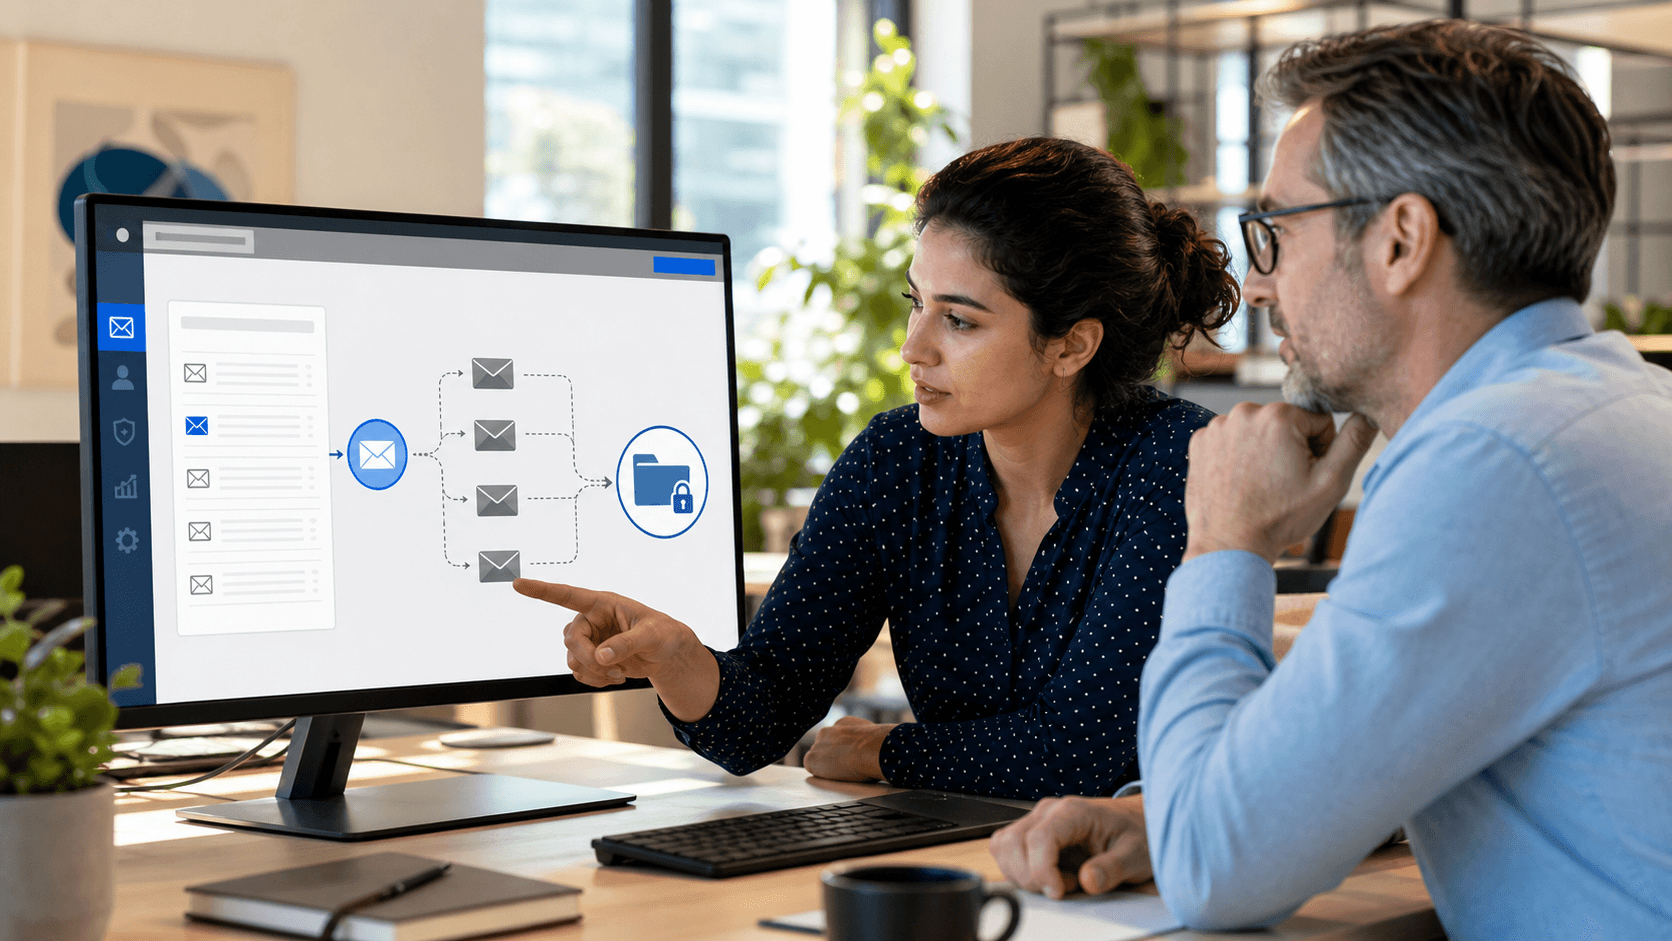
A malicious inbox, forwarding, or sweep rule can quietly:
- Move messages into archive folders, RSS feeds, deleted items, or obscure folders
- Mark messages as read so the user does not notice them
- Forward email to an unfamiliar external address
- Delete security alerts, password-reset notices, or MFA messages
- Hide messages tied to invoices, bank details, or customer requests
These rules can let an attacker remain informed even after a user changes a password. If the attacker is still receiving copied email, they may be able to watch ongoing conversations, learn who approves payments, and time an impersonation attempt.
The business risk grows during busy financial periods. As Q4 planning, renewals, purchasing, and year-end invoicing pick up in the fall, an overlooked mailbox rule can become more than an email problem. It can support payment diversion, executive impersonation, vendor fraud, or the exposure of customer and business information.
Rules Can Point to the Attacker's Goal
Forwarding rules are often a strong signal of what an intruder hoped to collect. A rule that sends messages to an unfamiliar external address may indicate that someone wanted to monitor contracts, invoices, legal correspondence, customer records, executive messages, or account-reset notices.
Still, forwarding alone is not proof of wrongdoing. Some teams have valid business reasons for approved forwarding. We compare the destination address with your authorized users, known workflows, and documented business processes before drawing conclusions.
Rules that hide messages can be equally revealing. Attackers may target words and phrases such as "invoice," "payment," "wire," "bank," "security," "MFA," or "Microsoft." Moving those messages away from the inbox can keep the user from seeing warnings while the attacker continues watching the account.
A rule focused on a particular vendor, finance employee, customer domain, or executive can suggest a payment-fraud objective. It may show that the attacker was waiting to:
- Intercept an approval request
- Change payment instructions through impersonation
- Monitor a high-value vendor conversation
- Suppress replies that could expose the fraud
- Learn internal payment and approval habits
The name of a mailbox rule is rarely enough to explain it. We need the conditions, actions, destination, creation time, and related email activity. Together, those details help separate an unusual but legitimate rule from one built to cause harm.
Evidence Rebuilds the Attack Timeline
After a report of a hacked Microsoft 365 account, timing matters. Evidence can change quickly as users clean up mailboxes, administrators make security changes, and retention settings remove older records. Preserving relevant details early gives the response team a better chance of understanding the full scope.
We typically review available mailbox rule settings alongside Microsoft Entra ID sign-in logs, audit logs, mailbox audit events, message trace results, email headers, conditional access records, and reports from affected users. What is available may vary based on licensing, logging settings, and your organization's record-retention policies.
Timestamps can connect events that might otherwise look unrelated. For example, a suspicious rule may have been created shortly after an unfamiliar sign-in, repeated MFA prompts, a password change, OAuth consent activity, a mailbox-forwarding update, or unusual outbound email.
That sequence can help us investigate possible access paths, including stolen credentials, phishing, token theft, an unmanaged device, or another method. It also helps identify whether the attacker acted once or kept returning to the account.
Scope is just as important as the first affected mailbox. Similar rules across several users may point to a broader campaign rather than an isolated event. During incident triage, we look for shared forwarding addresses, matching rule conditions, recurring IP addresses, unfamiliar devices, and common targets across mailboxes.
Containment Must Stop Harm Without Erasing Clues
The first task is to confirm whether a rule is authorized and document what it does. Before removing it, we want to capture its conditions, actions, destination addresses, folder paths, and timestamps. We also determine whether messages were forwarded, redirected, moved, marked as read, or deleted.
Depending on the findings, our containment work may include disabling the account temporarily, revoking active sessions and refresh tokens, resetting credentials, requiring MFA re-registration, blocking suspicious sign-ins, and removing malicious rules. Delegated mailbox access also deserves review, since unauthorized delegation can give an intruder another path into sensitive mail.
A full review should look for other persistence methods, including unauthorized OAuth applications, alternate authentication methods, mailbox-forwarding changes, and compromised administrator accounts. Removing one bad rule without checking for these related issues can leave a door open.
Payment-related exposure calls for fast, careful communication. Finance, accounts payable, leadership, and affected vendors may need to know that a conversation was exposed. We recommend independently verifying bank-detail changes and payment requests through established phone numbers or known contacts, not through the email thread that may have been compromised.
At EFROS, we can coordinate incident triage, Microsoft 365 security actions, communications, and recovery as one accountable team under a unified SLA. Keeping technical containment and business response aligned helps reduce confusion when time is limited.
Turn the Findings Into Better Mailbox Resilience
Every suspicious rule should lead to a practical review of the controls around it. If external forwarding was involved, we may recommend limiting it, monitoring it more closely, or requiring approval for exceptions. If the attacker hid security messages, alerts for risky inbox-rule creation and unusual mailbox behavior can help bring the next attempt to attention sooner.
Longer-term safeguards often include phishing-resistant MFA where appropriate, stronger conditional access policies, reduced legacy authentication paths, mailbox auditing, centralized logging, and tested alert workflows. The right mix depends on how your people work and what information their mailboxes handle.
The attacker's target should also shape the response. Rules aimed at invoices may call for stronger payment-verification procedures. Executive-focused rules may signal a need to tighten impersonation protections and review access to sensitive correspondence. Forwarding of customer data can require a review of data-handling controls, notification duties, and applicable compliance requirements.
A Microsoft 365 account hacked event should be treated as a possible business-wide security issue, not a routine user-support ticket. Security Score can provide a quick, 60-second automated check of publicly available data only, while a paid Engineer Assessment can help evaluate your environment and priorities. The practical takeaway is simple: preserve the evidence, investigate the rule's purpose, contain related access, and use what you learn to make the next silent rule harder to create and easier to find.
Strengthen Your Microsoft 365 Defenses
If you are dealing with a Microsoft 365 account hacked incident, our team can help prioritize containment, investigation, and practical security improvements. EFROS provides paid Engineer Assessments to examine your environment, identify relevant risks, and build a focused path forward. For help coordinating next steps, contact us to discuss your situation with our team.